On the night of 11-12 October, attackers heated the fridges and freezers at Intermarché, Carrefour, Monoprix, Leclerc and Coopérative U stores across France to around 50°C. Intermarché CEO Thierry Cotillard put the losses at “tens of millions of euros nationwide in a single day”. Danfoss, the Danish manufacturer whose controllers ran many of those cold rooms, says most of its own units that were hit were the AK-SM 800 and AK-SC 355, models it stopped updating in 2021 and 2016.
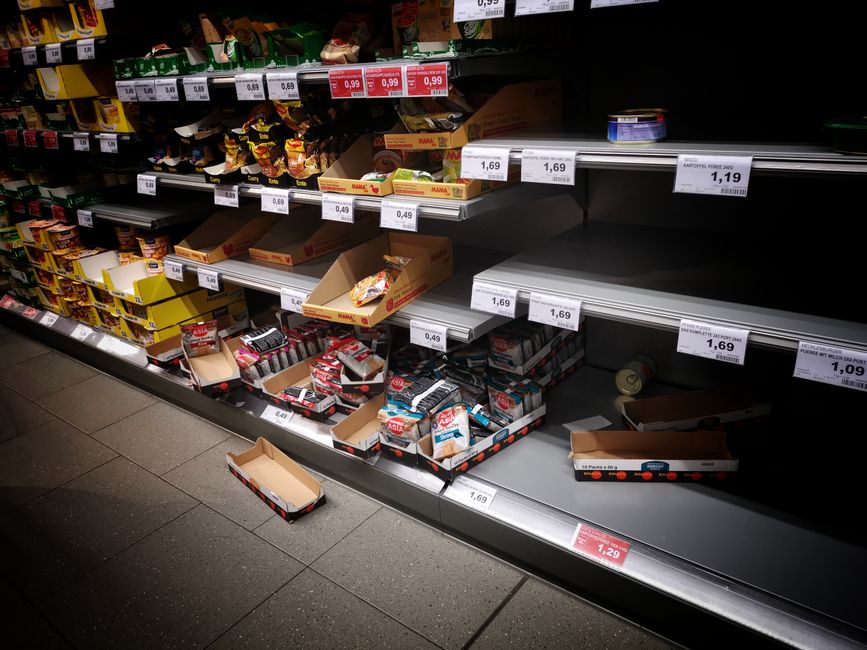
The stock spoiled, and in some stores the heat started fires. For most of the Danfoss units hit, by Danfoss’s own account, there was no fix to install.
Danfoss is an industrial manufacturer. Its AK-SM and AK-SC controllers sit in a store’s back room and run the whole cold system: each cabinet’s temperature, its alarms, its defrost schedule, all adjustable by an engineer working remotely. The attackers got into that box and told the fridges to defrost. They stretched defrost cycles from one hour to eight so the alarms stayed quiet, and one store reached 80°C. Intermarché’s owner, Les Mousquetaires, said its stores were held at 50°C for six hours.
The store counts differ depending on which outlet the chain spoke to:
| Chain | Stores reported hit |
|---|---|
| Les Mousquetaires (Intermarché) | ~150 (The Register, ABC); ~180 (TIME) |
| Carrefour | ~80 (The Register, TIME) |
| Coopérative U | 80 of 2,000 (The Register); at least 100 (TIME) |
| Monoprix | about 5% of its 490 stores (The Register); 30 (TIME) |
| Leclerc | named as hit, no count given (BleepingComputer) |
Totals run from 250-350 stores, per French outlets cited by BleepingComputer, to about 500, per Cooling Post.
The money is still being counted. Les Mousquetaires puts its own losses at “several million euros”. TIME reports €270,000 lost across two stores in Alsace, while SOCRadar puts the same €270,000 at a single store in Haguenau. No one has claimed responsibility, and SOCRadar found nothing linking the group NoName057(16) to the attack.
One fact cuts against the single-product explanation. Coopérative U CEO Dominique Schelcher told RTL that Coopérative U is not a Danfoss customer, even though 80 or more of its stores were hit. Coopérative U has not said what failed in those stores.
End-of-life units and patches more than a year old
Danfoss’s first answer was that the affected stores “were running outdated firmware” and that it has always advocated keeping systems updated. That statement assigns the problem to the stores. The company’s fuller account, to Cooling Post and to franceinfo, describes the hit fleet differently:
“The majority of the devices concerned are obsolete products, notably the AK-SM800 and AK-SC355 systems.”, Danfoss, to franceinfo
Danfoss declared the AK-SM 800 end of life in May 2021 and phased out the AK-SC 355 in 2016. Neither model gets software or security updates. For most of the controllers that cooked the stock, “outdated firmware” describes a product with no newer firmware to install.
The remaining units were AK-SM 800As, the current model, and they had not been patched. On 20 May 2025, the US cybersecurity agency CISA published advisory ICSA-25-140-03. It covered CVE-2025-41450, an authentication bypass rated 8.2 out of 10, which was fixed in release R4.2. CISA updated the advisory on 26 August 2025 to add a command-injection flaw and a configuration flaw, both fixed in release 4.3.1. Danfoss issued its own advisories, DSA-2025-03-01 and DSA-2025-08-01, over the same period. From the first advisory to the attack is roughly 17 months.
The bypass was crude. CISA credits Tomer Goldschmidt of Claroty’s Team82 with finding it. The AK-SM 800A had a hidden login that accepted a code generated from the current date, and it worked regardless of the administrator password. Anyone who reproduced the algorithm could produce that day’s code. Claroty published the full “code-of-the-day” research on 9 August 2026, and Zscaler followed on 20 August. A public, scriptable way past the password was in circulation for about eight weeks while 800A units sat unpatched. Security researcher Kevin Beaumont called it “a zero-skill thing to pull off.”
For most of the controllers that cooked the stock, “outdated firmware” describes a product with no newer firmware to install.
That bug shows how weak this product family’s security was. Authorities have not identified the entry point, there is no record linking the attack to Claroty’s flaws, and the CISA advisory did not cover the end-of-life models that made up most of the damage. Prime Minister Sébastien Lecornu’s office said ANSSI, France’s national cybersecurity agency, had pinpointed a flaw in Danfoss software. It did not say which one.
CERT-FR, the French government’s computer emergency response team, issued alert CERTFR-2026-ALE-012. It reported compromises of AK-SM and AK-SC controllers that neither Claroty’s research nor Danfoss’s advisories had mentioned.
Zscaler noted, before the attack, that cold-chain operators delay updates because a maintenance window can mean spoiled product. That excuse covers only the AK-SM 800A minority. For the end-of-life majority there was no patch to delay, so maintenance-window risk explains nothing about why those units were hit.
Danfoss’s 12 October statement promised “firmware updates where available”, along with stronger network protections and removing direct internet exposure. For most of the units that were hit, an update is not available.
Thousands of controllers still online, mostly in France
The controllers were online because that saves money. Claroty CTO Amir Preminger described the trade-off:
“While this convenience significantly reduces maintenance costs by allowing engineers to troubleshoot issues remotely, it also lowers the barrier to entry for attackers.”
The stores saved on engineer visits, and the risk came with that saving. When the risk materialised, retailers lost the stock and shoppers found empty fresh aisles. The same pattern turned up in exposed industrial control interfaces in Venice. The step from software access to physical damage is one this field has understood since Stuxnet turned code into broken centrifuges.
The exposure was measured before the attack. On 19 August, a Shodan query cited by Zscaler found 3,726 Danfoss management interfaces on the public internet. Shodan is a search engine that indexes devices connected to the internet. Team82 counted about 2,800 using Censys, a similar search engine.
After the attack, the count was still in the thousands. Shodan showed more than 4,500 exposed endpoints, more than half of them in France, and SOCRadar put France’s share higher still. The totals depend on the query:
- Cybersecurity News found 4,980 hosts (4,551 with a filtered query), including 2,911 in France.
- SOCRadar counted 2,898 French results on 13 October, about 65% of the global total.
- BleepingComputer reported a lower figure: 2,752 worldwide and 1,590 in France.
France was not the only country hit. Spain, Portugal, Poland, Germany and Belgium also reported affected sites. In late August, refrigerators at US military commissaries in several states went into defrost mode and spoiled thousands of dollars of food. Army, Air Force and Pentagon investigators are looking into those outages, and no Danfoss link has been established.
CERT-FR’s advice for a suspected compromise is a factory reset, security patches, new credentials and full reconfiguration. For an AK-SM 800 or AK-SC 355, the patch step does not exist. The only real fix is a new controller, and that bill lands on the retailers, not on Danfoss. Meanwhile somewhere between 1,590 and 2,911 French controllers were still reachable from the internet after the attack, depending on the query, and nobody has named the way in. Nothing on the record stops the same night from happening again.
The Paris prosecutor has opened an investigation, and ANSSI is investigating nationally and at EU level after Lecornu tasked it with the case. France’s retail federation, the FCD, has asked Danfoss for “full transparency”. The flaw ANSSI says it has found would be a reasonable place for that transparency to start.
Further Reading
- Cyberattacks crank French supermarket refrigeration systems up to 50°C, The Register on store counts, Danfoss’s firmware claim, Claroty’s date-code bug and Coopérative U’s denial.
- ICS Advisory ICSA-25-140-03: Danfoss AK-SM 8xxA Series, CISA’s 2025 advisory listing the AK-SM 800A flaws and fixed releases.
- Cyberattack shuts down refrigerators at French supermarkets, BleepingComputer on chains hit and the Paris prosecutor’s investigation.
- Danfoss moves to mitigate cyberattack, Cooling Post on Danfoss’s statement and its end-of-life models.
- French fridge attack: Danfoss says most hit units were end of life, Danfoss’s franceinfo statement and the missing link to Claroty’s flaws.
- ‘Unprecedented’ Cyberattack Targets French Supermarket Fridges, TIME on stretched defrost cycles, 80°C readings and losses.
- Hackers raise fridge temperatures at hundreds of French supermarkets to spoil food, ABC on the six-hour 50°C hold and other affected countries.
- Danfoss Refrigeration Hack Update – 4,980 Hosts Found Exposed to Internet, Shodan exposure counts by country.
- French Supermarket Cyberattack: Exposed OT Behind France’s Food Supply, SOCRadar’s count of exposed French controllers.
- The fix has been out a year, the controller is still exposed, Zscaler’s pre-attack warning on exposure and why operators delay patching.
- Army, Air Force special agents investigate refrigerator outages affecting commissaries, Stars and Stripes on the August US commissary outages.
- Refrigeration cyberattack hits French supermarkets, Cybernews on end-of-life units and ANSSI’s unnamed Danfoss flaw.